Share authority
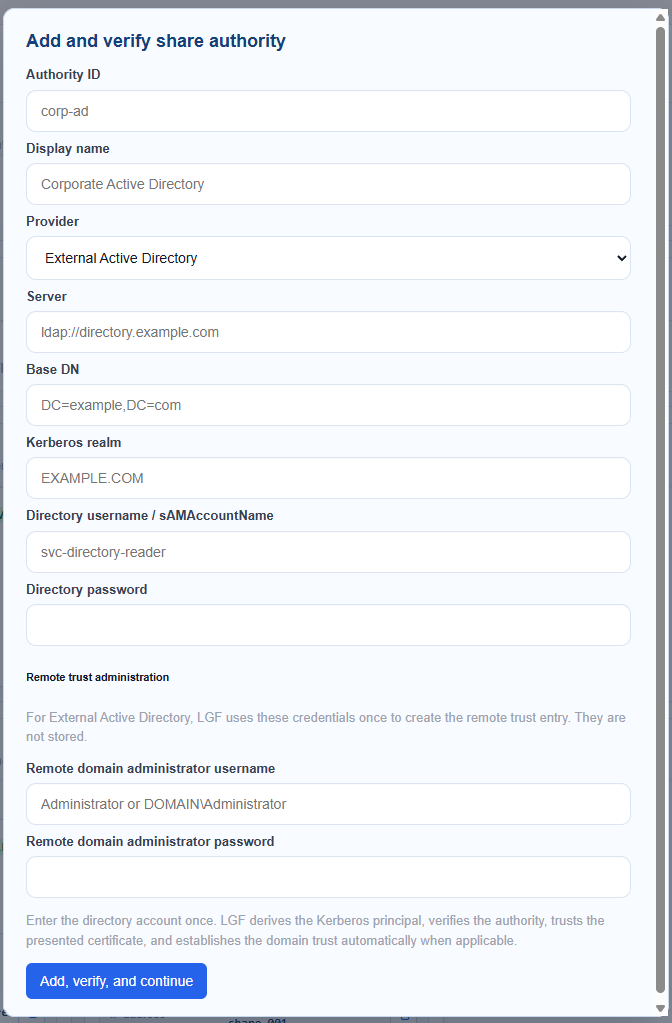
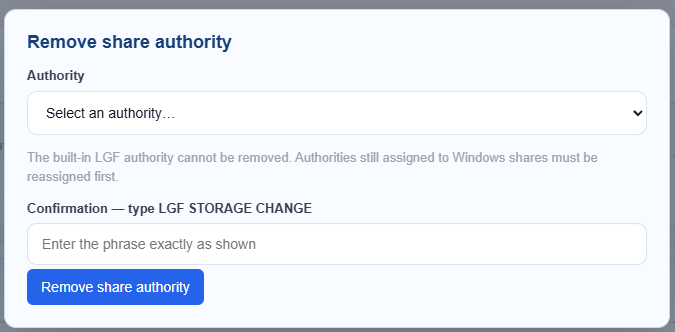
Windows shares are grouped by their explicit share authority. Choose the authority that should validate users and groups before creating or editing a share. The authority may be the framework-owned Samba domain or another configured identity source.
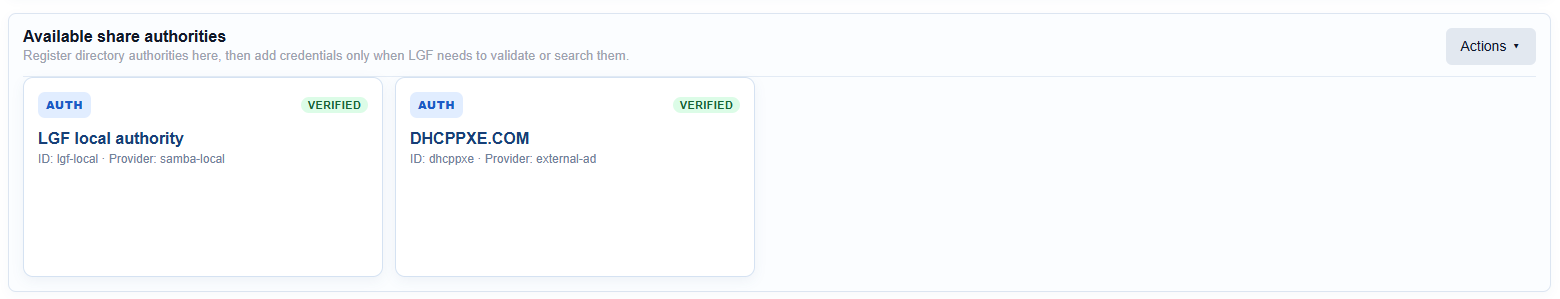
The authority controls how clients authenticate; it does not change the share's filesystem permissions. Configure both the identity mapping and the underlying directory permissions.
Groups and permissions
Use domain groups for repeatable access policies. Grant the minimum required share and filesystem permissions, and test with a normal user account before distributing the share address.
If a client is not joined to the domain, it may need an explicit username format and NTLM-compatible authentication. Domain-joined clients should use the AD DNS name so Kerberos can be used where available.