Users and groups
Domain users and groups provide the identity layer for Windows access, operator login, and share permissions. Use groups for role assignment so that access can be reviewed and changed without editing every service individually.
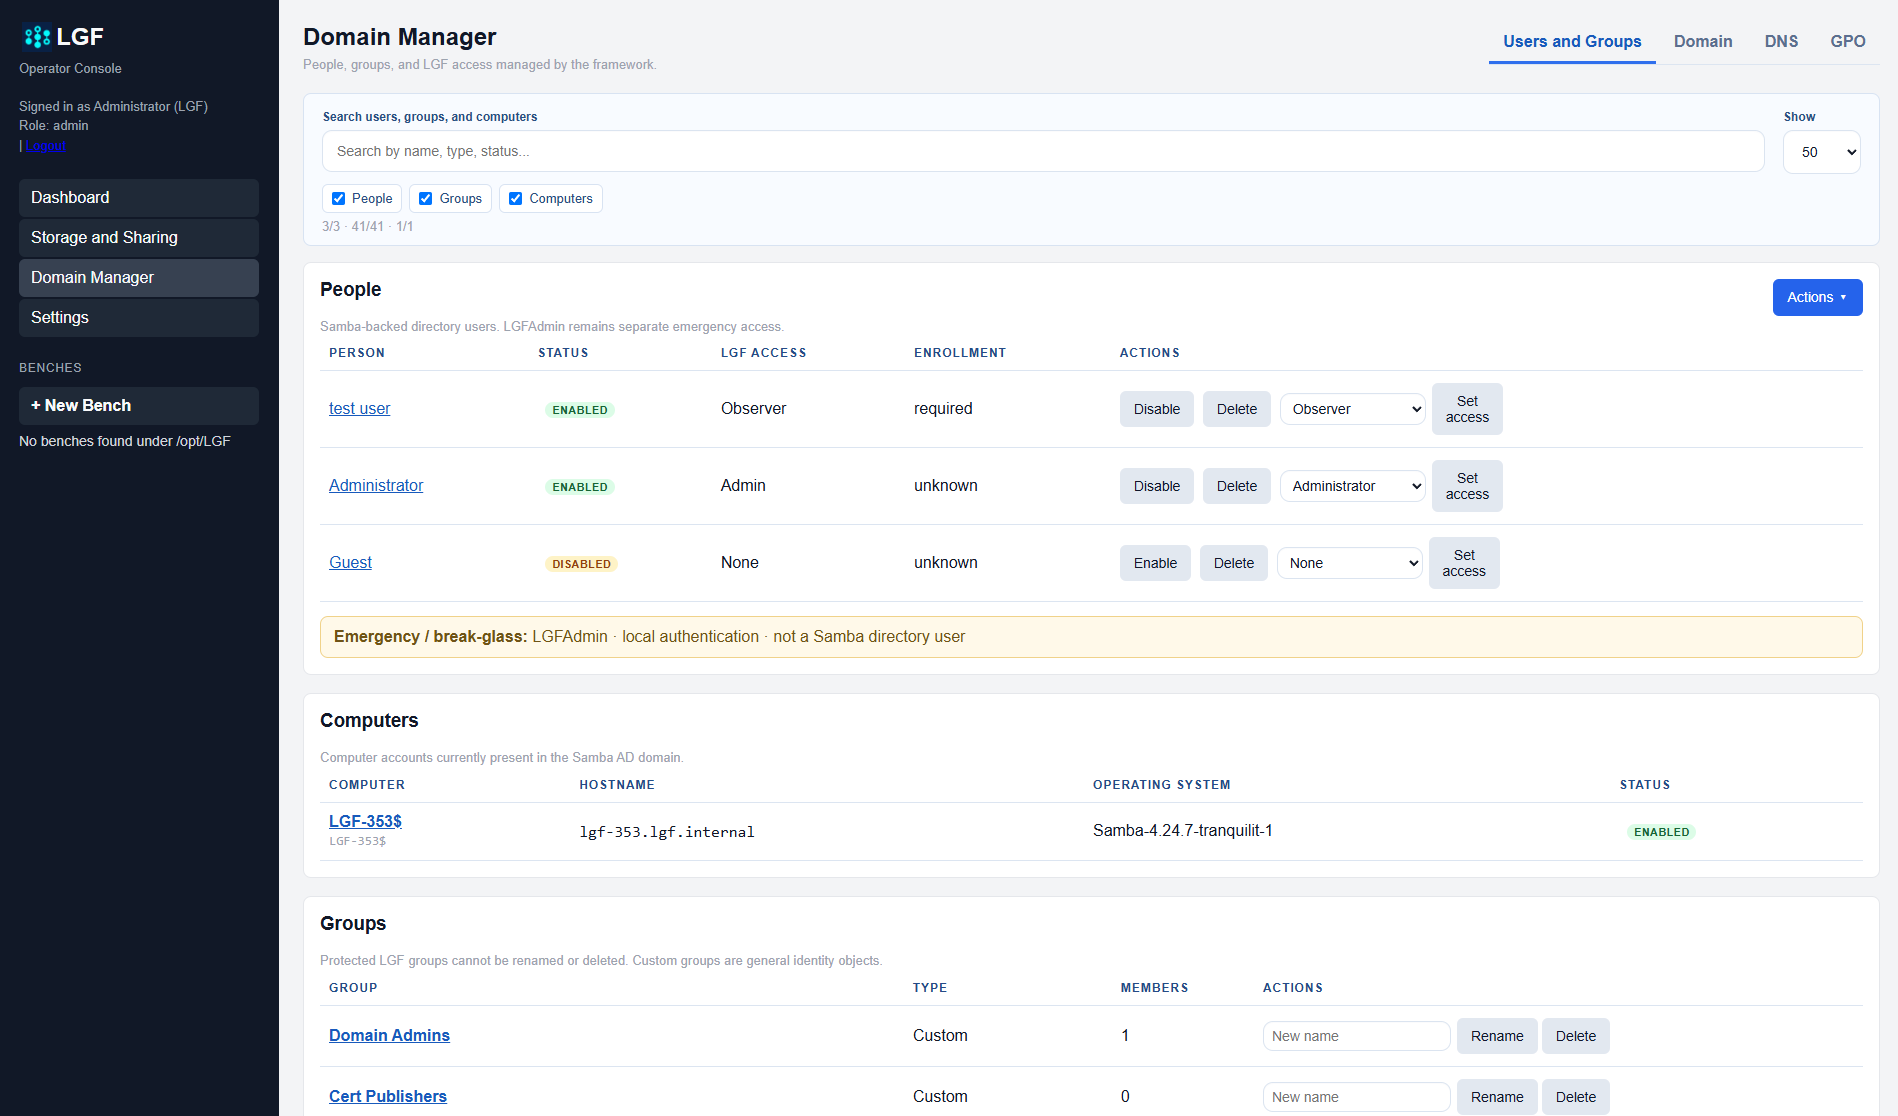
LGF includes default groups and RBAC mappings for the operator console. A domain-join workflow inherits those existing mappings; it should not require recreating the framework's default roles on every host.
Safe administration
- Create named operator accounts instead of sharing the break-glass account.
- Grant the smallest role required for each operator.
- Use groups for recurring access such as Windows shares.
- Verify membership changes with a test login before removing an existing administrator path.